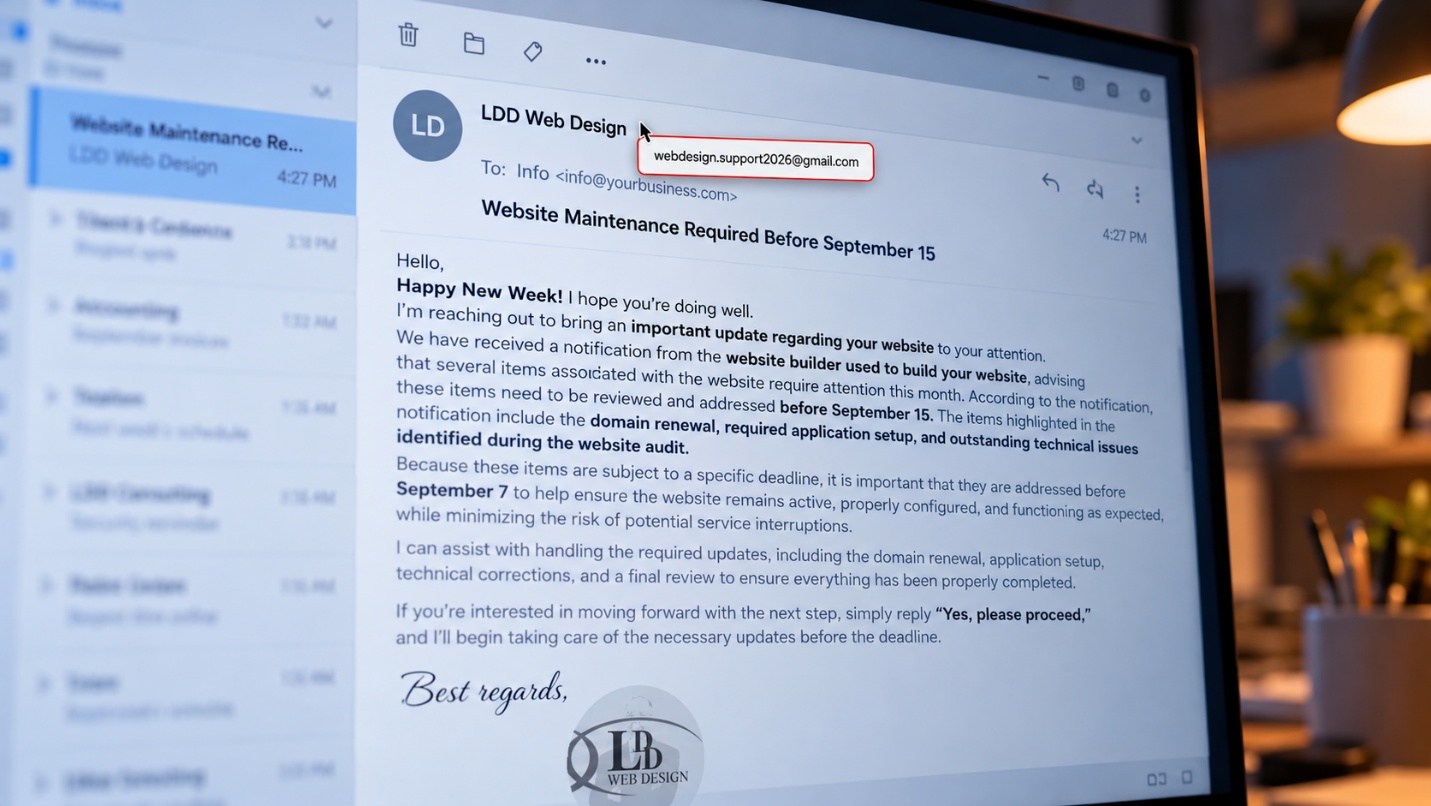
Business impersonation scam email from LDD Web Design revealed as a Gmail address when hovering over the sender name

Scammers Impersonated Our Company: How the Scam Worked

In September, scammers sent 15 to 20 of our own website clients a series of emails pretending to be us. They copied our LDD Web Design logo, wrote in a friendly professional tone, and asked for $600 for “required” website updates. The emails came from a Gmail address, not from our domain. If a vendor you work with ever emails you about an urgent problem and a payment, verify it by calling a number you already have before you reply.
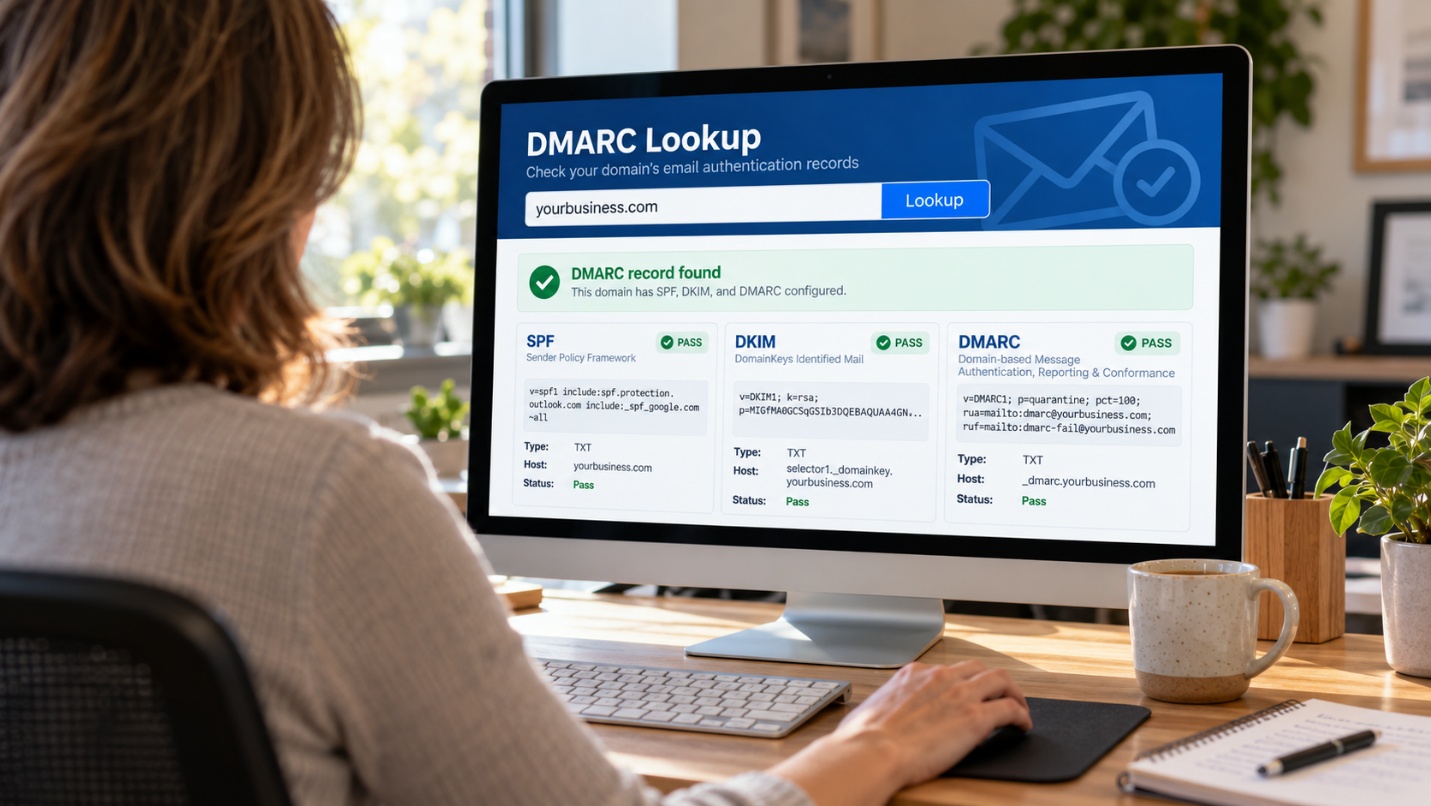
SPF, DKIM, and DMARC records checked for a small business email domain

Can Someone Send Email as Your Business? SPF, DKIM & DMARC

Yes. Unless your domain has three settings in place, anyone can send an email that appears to come from your exact address. SPF, DKIM, and DMARC are DNS records that tell receiving mail servers which messages really come from your business and what to do with the ones that don’t. Setting them up correctly is usually a one-time project, and it protects your customers, your vendors, and your reputation.

A fishing hook above a wrapped holiday gift on an office desk, illustrating holiday phishing scams

Holiday Phishing Scams to Warn Your Team About

Phishing picks up as the holidays approach. Inboxes fill with shipping notices, year-end invoices, and gift requests, and busy, distracted employees are more likely to click before they think. Scammers know this and time their messages to match. A short briefing with your team before the rush — what the common scams look like, what the red flags are, and exactly who to tell when something seems off — is one of the cheapest, most effective defenses a small business has.

A person repairing a bicycle tire on an autumn trail

Patch Management for Small Businesses: A Simple Routine

Most successful attacks don't rely on anything clever. They exploit known security flaws that already have a fix — on machines that never got it. Patch management is the routine that closes those gaps: knowing what needs updating, installing updates on a predictable schedule, and confirming they actually worked. It isn't glamorous, but it's one of the most effective security habits a small business can have.

Expired parking meter marked valid through October 13, 2026 on an autumn street

Windows 10 ESU Year 1 Has Ended: What Now?

Windows 10 support ended in October 2025. Since then, many businesses have kept their Windows 10 PCs patched through Microsoft's paid Extended Security Updates (ESU) program. Year One of that coverage ended on October 13, 2026. Business PCs without Year Two coverage no longer receive security fixes. They still turn on and run normally, but every month without updates adds risk. You can still buy Year Two — you'll pay for Year One too — or use this as the push to finish moving to Windows 11.

Cyber Insurance Readiness What Insurers Require

Cyber Insurance Readiness: What Insurers Require

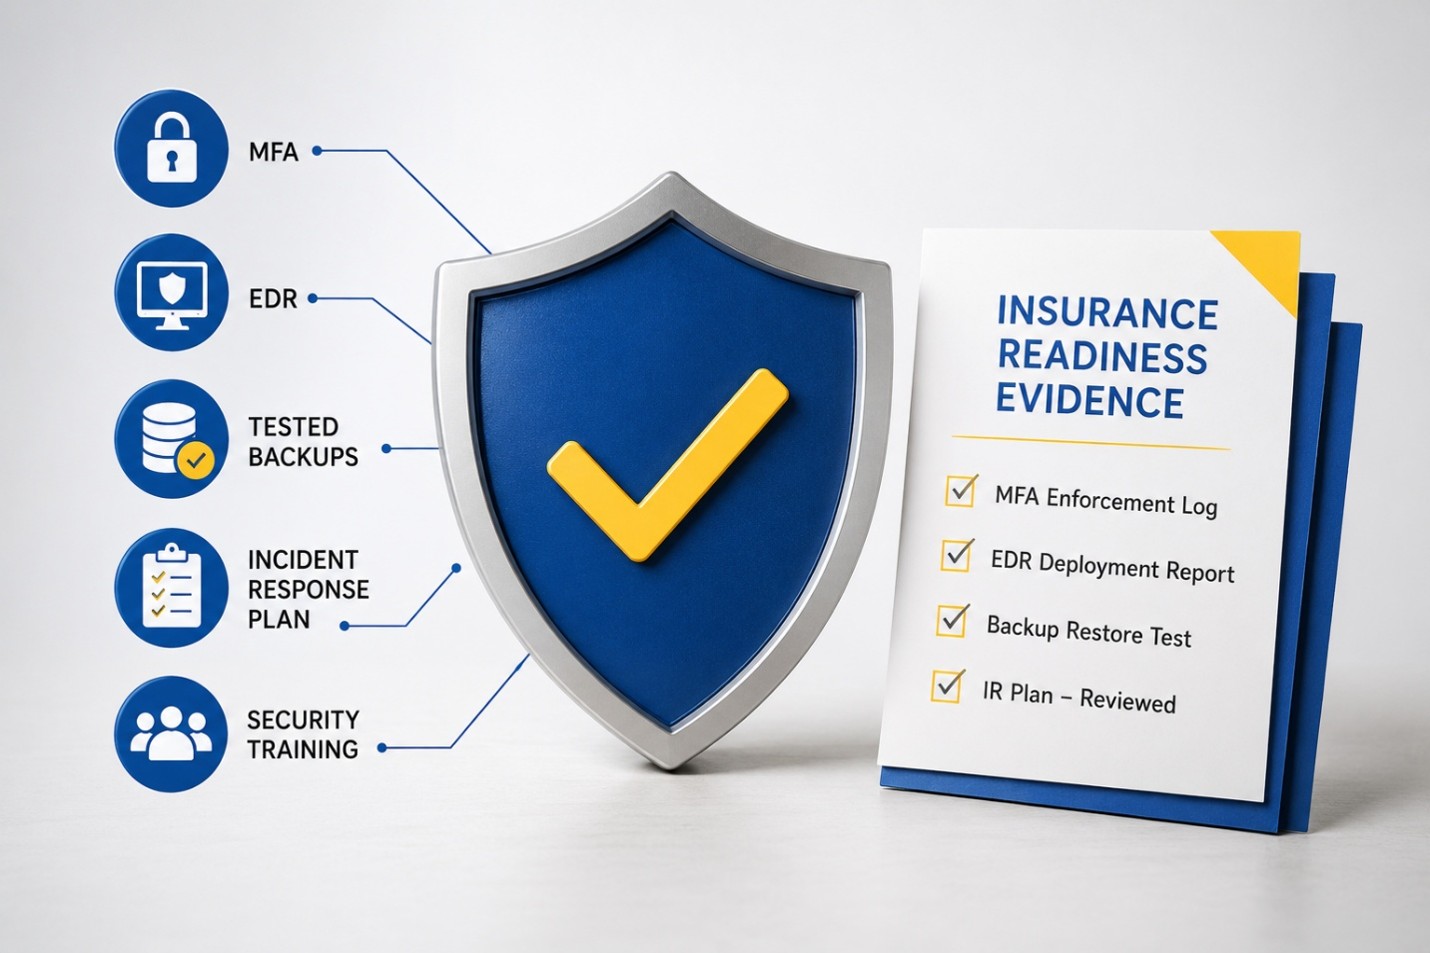
Cyber insurance used to be a simple application and a check. Today, insurers require documented proof of specific security controls — multi-factor authentication, endpoint detection and response, tested backups, and a written incident response plan — before they’ll write or renew a policy.

Business Continuity vs. Disaster Recovery

Business Continuity vs. Disaster Recovery: Key Differences

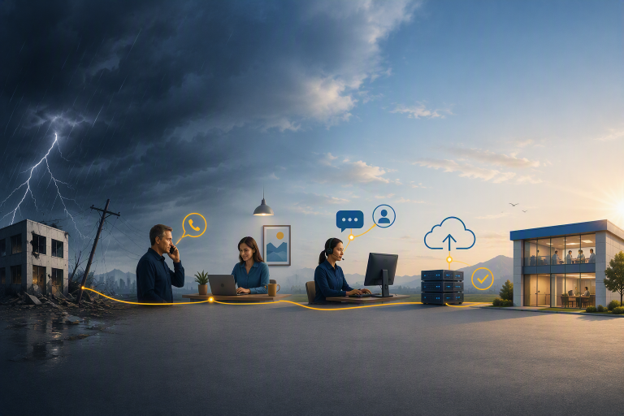
Disaster recovery is about getting your systems and data back — restoring servers, files, and applications after something goes wrong. Business continuity is bigger: it’s how your entire business keeps functioning while that recovery happens — who talks to customers, where staff work from, how payroll gets processed, which vendors step in.

Shadow IT and Shadow AI

Shadow IT: The Apps Your Employees Are Using Without Telling You| LDD Consulting

Shadow IT is any app, tool, or service employees use for work without IT’s knowledge or approval — a personal Dropbox account, a free project management app, an AI chatbot used to summarize a client contract. It usually starts with good intentions: someone wants to work faster and doesn’t want to wait on an approval process. But every unapproved tool is a blind spot — data your IT team can’t secure, back up, or even see.

Vacation Season Is Peak Season for Cyberattacks

Vacation Season Is Peak Season for Cyberattacks — Here’s Why | LDD Consulting

Cybercriminals don’t take vacation — and they know when your team does. The FBI and CISA have specifically warned that attackers time major ransomware attacks to coincide with holidays and long weekends, precisely because network defenders and IT support are running at limited capacity. Summer vacation schedules create those same conditions for weeks at a time: slower detection, easier impersonation, and more time to move through your systems before anyone notices.

Is Your Incident Plan Actually Going to Work

Is Your incident Response Plan Actually Going to Work? | LDD Consulting

The only way to know if your incident response plan will actually work is to test it before a real attack forces you to find out. A tabletop exercise — a structured walkthrough where your team responds to a simulated cyberattack scenario — exposes the gaps, unclear roles, and outdated contact info that live inside every untested plan. Businesses that skip this step often discover their plan fails at the exact moment they need it most.